SimplyMobile is now ISO/IEC 27001:2022 certified
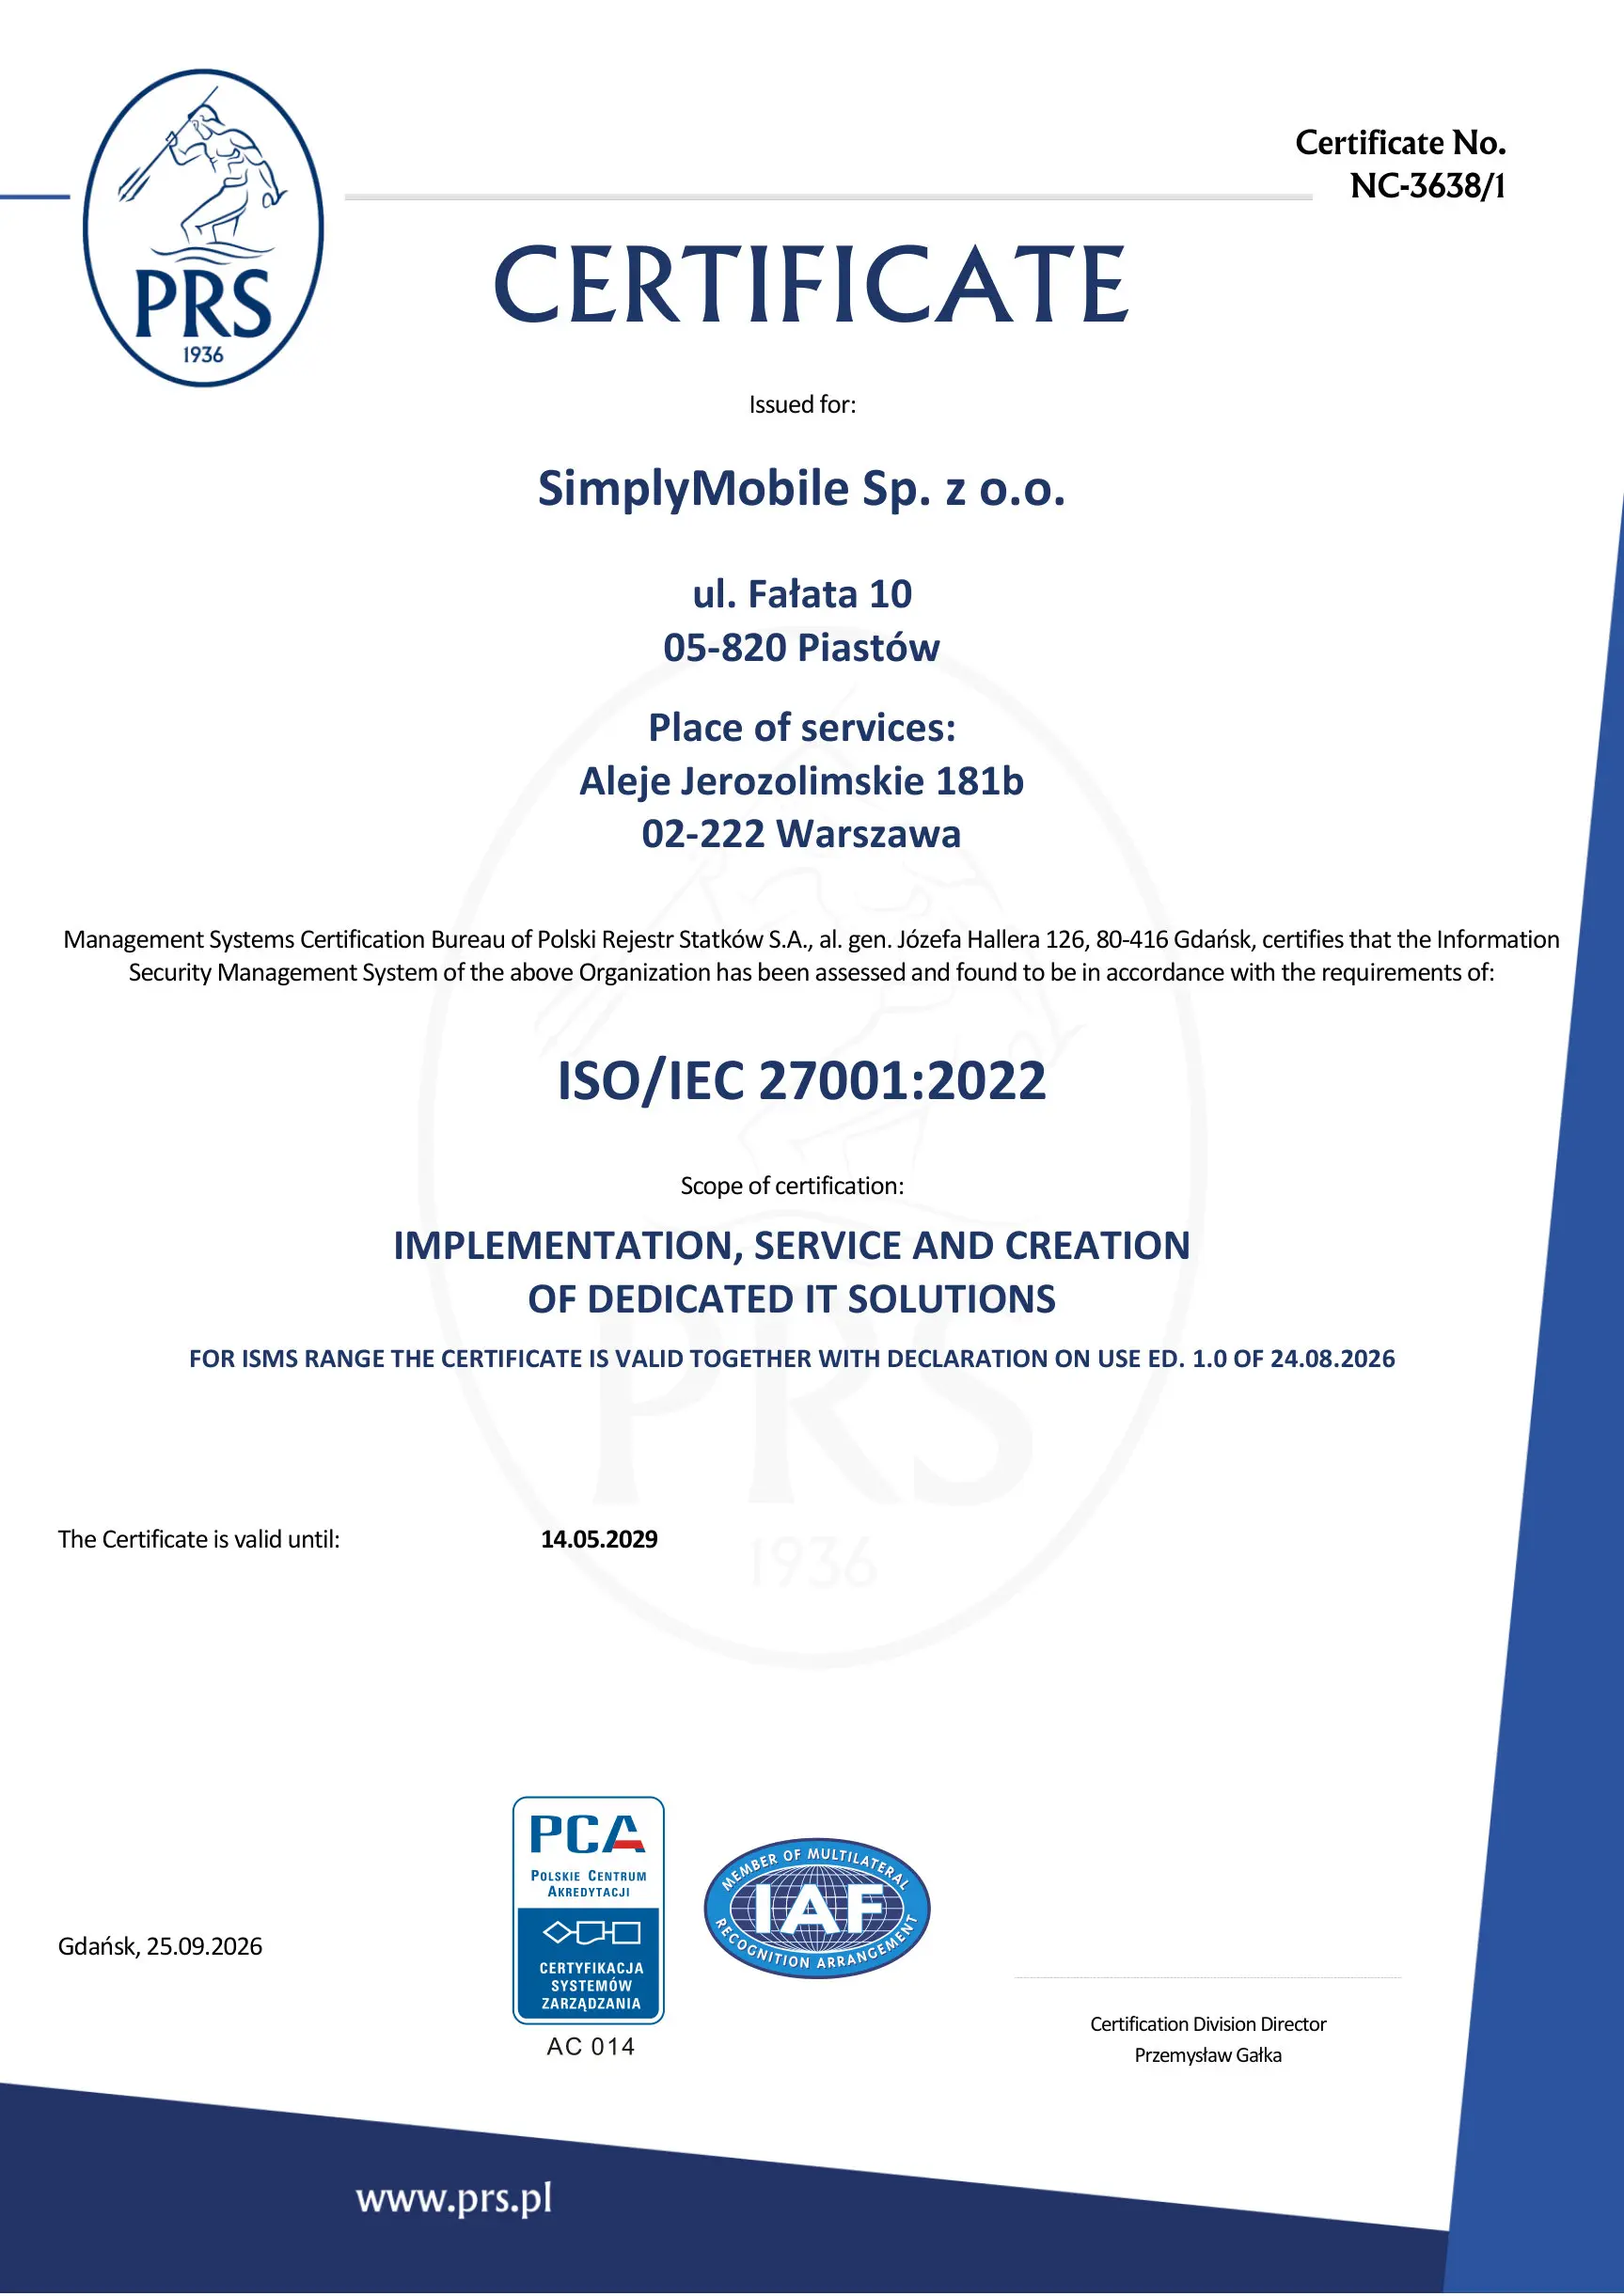
Our information security management system (ISMS) has been independently assessed and confirmed with the ISO/IEC 27001:2022 certificate. It is formal proof that we process our clients' data based on audited security processes.
We have treated our clients' data security as a priority for years. Now an independent audit confirms it: SimplyMobile's information security management system meets the requirements of the international standard ISO/IEC 27001:2022.
What ISO/IEC 27001 is
ISO/IEC 27001 is the leading international standard for information security management. It defines how to identify risks in a structured way, protect data (confidentiality, integrity, availability) and continuously improve safeguards - within an Information Security Management System (ISMS).
Certification means an independent, accredited body has reviewed our processes and confirmed they conform to the standard. It is not a one-off check - the standard requires regular surveillance audits and continuous improvement.
What our certificate covers
- Standard: ISO/IEC 27001:2022
- Scope: implementation, service and creation of dedicated IT solutions
- Certification body: Polski Rejestr Statkow S.A. (PRS), PCA accreditation no. AC 014, IAF recognition
- Certificate no.: NC-3638/1
- Valid until: 14.05.2029
What it means for clients
- Better data protection - your data in the CMMS is protected in line with a recognised international standard.
- Audited processes - security is a repeatable, verified process for us, not a declaration.
- Compliance support - we make it easier to satisfy your audits, security teams and regulations (NIS2, GDPR).
- Secure cloud - our deployments on Microsoft Azure are covered by the same information security management system.
ISO 27001 and NIS2
The NIS2 directive raises cybersecurity requirements for many companies and their suppliers. ISO/IEC 27001 is a natural foundation for compliance - it covers risk analysis, incident management, supply-chain security and business continuity that NIS2 requires.
If you assess your suppliers' security, our ISO 27001 certificate is a ready answer. We write more about it in the article on NIS2 supplier assessment and on the ISO / NIS2 portal page.
You can view and download the certificate on the Certifications and Quality Policy page.
Frequently asked questions
- Who issued the ISO 27001 certificate for SimplyMobile?
The certificate was issued by Polski Rejestr Statkow S.A. (PRS) - an accredited certification body (Polish Centre for Accreditation, accreditation no. AC 014, IAF recognition). PRS confirmed that our information security management system conforms to ISO/IEC 27001:2022.
- What is the scope of the certification?
The scope covers implementation, service and creation of dedicated IT solutions - exactly the area in which we deliver and maintain the SimplyMobile system for our clients.
- Until when is the certificate valid?
The certificate (no. NC-3638/1) is valid until 14.05.2029, subject to positive surveillance audits carried out periodically by PRS.
- Does ISO 27001 help with NIS2 compliance?
Yes. ISO/IEC 27001 covers key requirements addressed by the NIS2 directive - risk analysis, incident management, supply-chain security and business continuity. Our certificate makes it easier to assess SimplyMobile as a supplier in your compliance process.
- Where can I see the certificate?
The certificate is available as a PDF on the Certifications and Quality Policy page.
See SimplyMobile in action
Book a free, no-obligation demo — we'll show the system on your own processes.